Making compliance work in the real world
Embedding measurable behaviour change into everyday work to prove compliance and strengthen security.

Compliance expectations
are changing
A new regulatory landscape
Security leaders don’t need more noise around compliance, especially as the UK prepares for significant regulatory change. The forthcoming Cyber Security and Resilience (Network and Information Systems) Bill is set to overhaul the existing NIS Regulations, expanding the range of regulated organisations, strengthening incident-reporting duties and increasing regulators’ powers. As a result, organisations will face greater expectations and closer scrutiny.
Proof, not process
In this changing environment, leaders need clarity and credible evidence that their controls, training and interventions genuinely work. Confidence no longer comes from completing processes or ticking boxes. It comes from demonstrating that security measures are effective in the real world and that people understand and act on their responsibilities.
Get the assurance that compliance works
When leaders and auditors evaluate your security posture, they’re not looking for checklists or rigid adherence to traditional interventions. They want assurance that your organisation operates securely day to day and can demonstrate this, backed by clear evidence that it meets its requirements in a logical, proportionate and effective way for your environment.

People understand their responsibilities

Training is aligned with the real level of risk

Controls function effectively in practice, not just
on paper

Control activities are consistently measured
and measurable
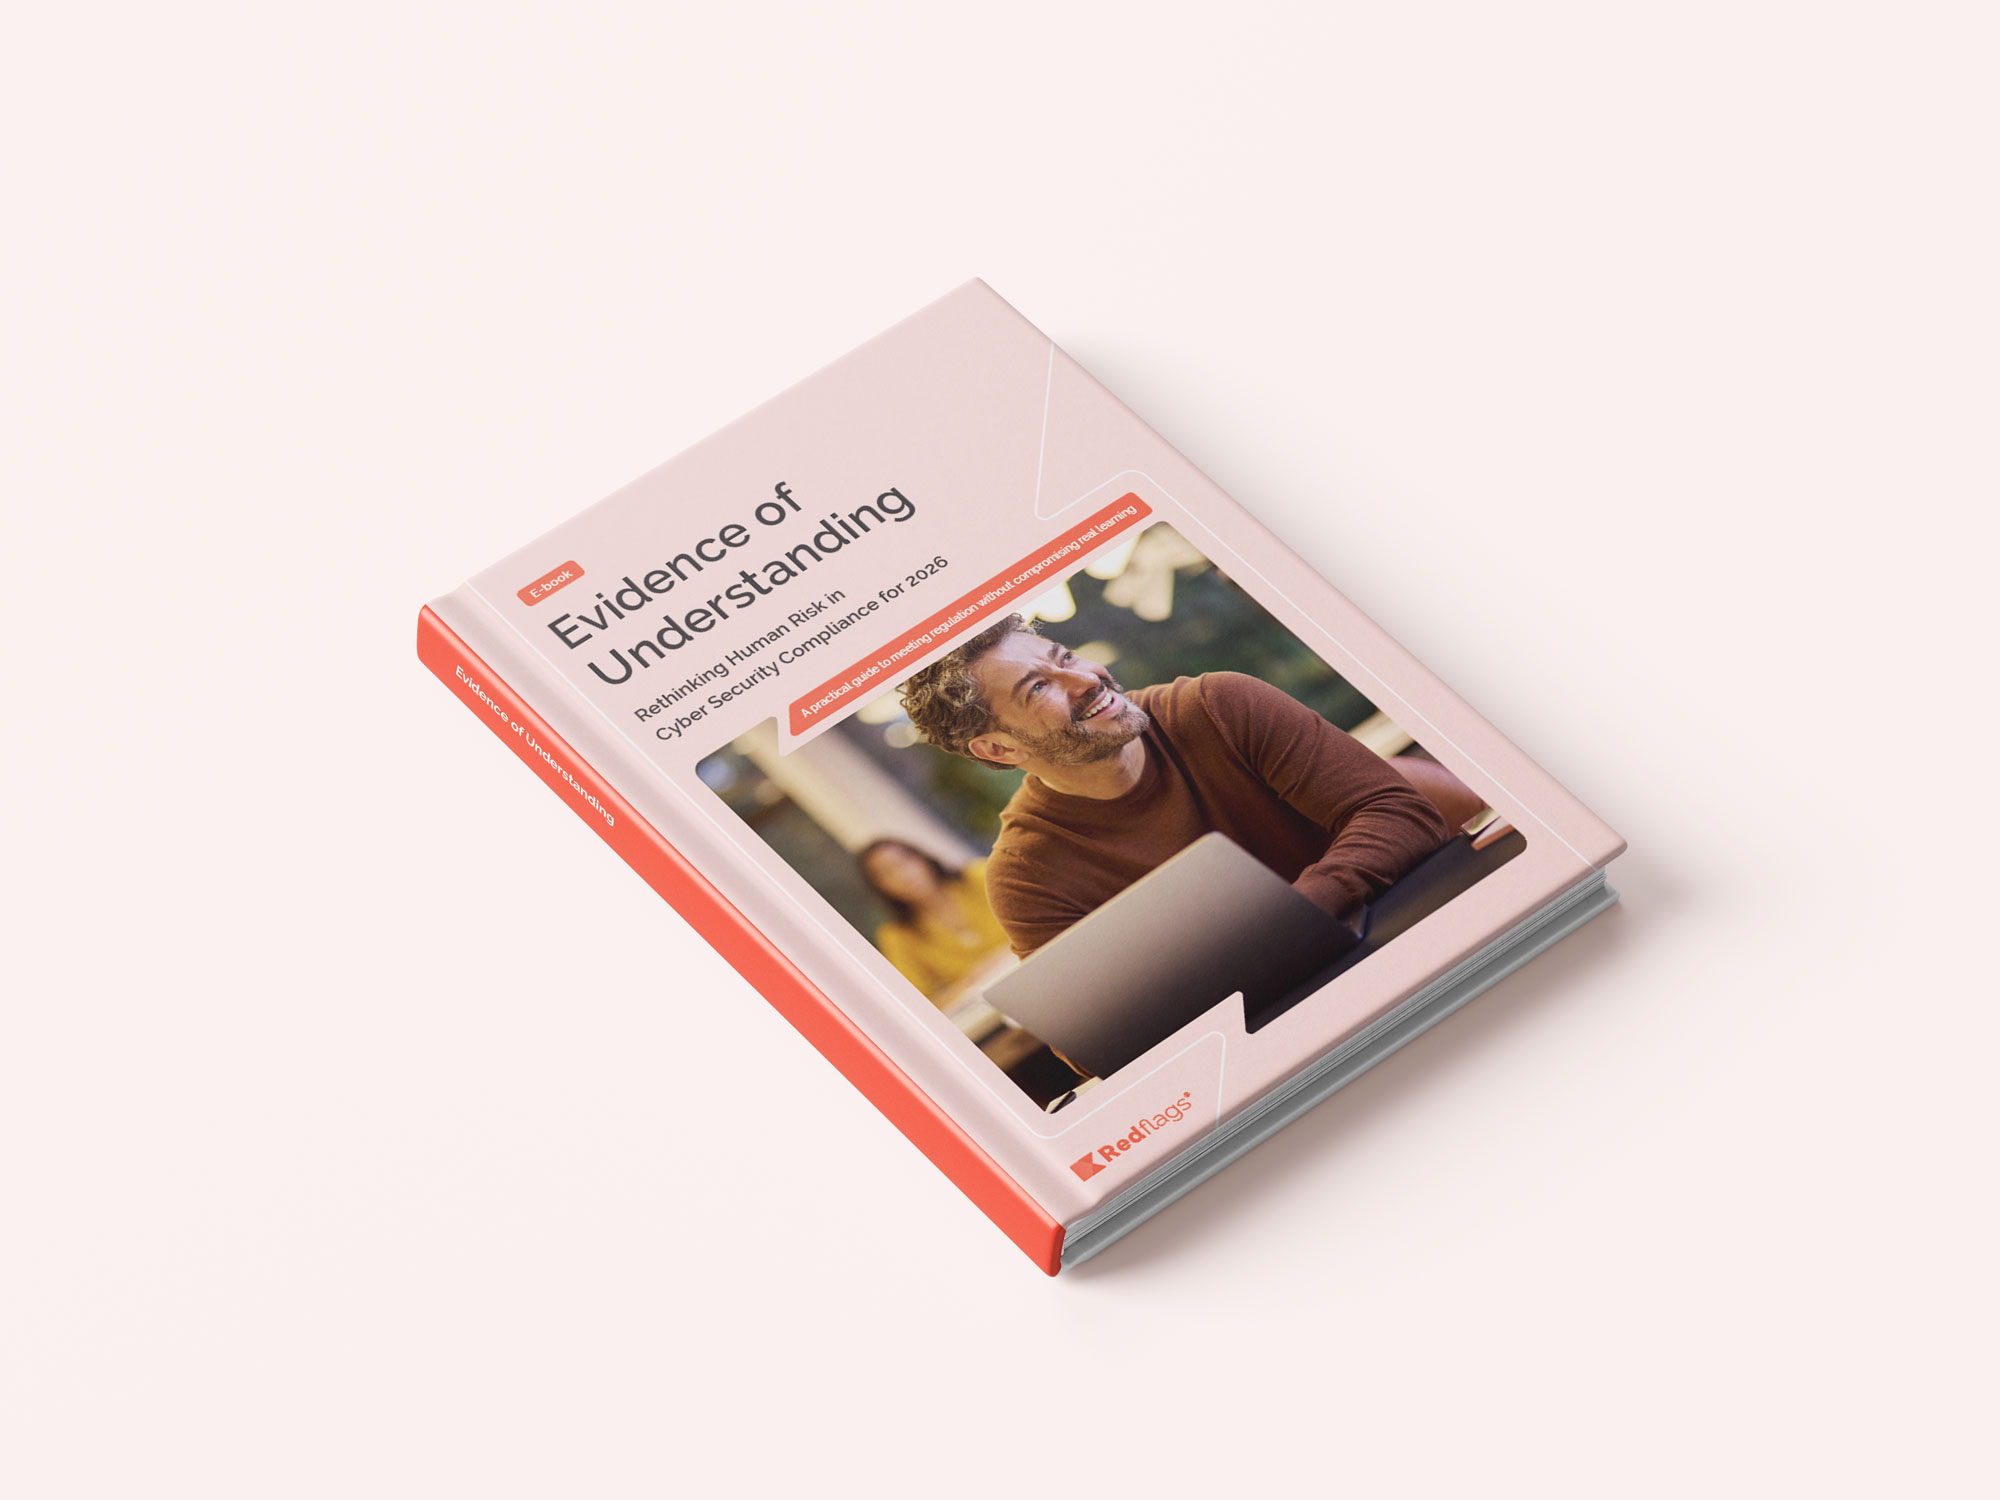
Evidence of Understanding
Move beyond checklists to
meaningful, ongoing interventions
Traditional security awareness activities such as annual training, phishing simulations, policy sign-offs, broadcast communications, and periodic testing are familiar for a reason. They’ve been embedded, reinforced through standards guidance, and adopted by every organisation. But familiarity doesn’t equal effectiveness. Modern compliance demands more than repeating activities annually. It requires continuous insight, behavioural assurance, and evidence that your controls are working—not just during audit season, but every day. This is where a new approach becomes essential: one that replaces box ticking with evidence-driven, ongoing interventions that strengthen organisational resilience.


Use the Redflags advantage
Redflags gives organisations a way to finally close the gap between training delivered and training that actually changes behaviour. Instead of relying on annual courses or one-off activities, Redflags brings compliance into the flow of work with real-time interventions that matter at the moment of risk.
When an employee is about to make a risky decision (clicking a suspicious link, mishandling data, bypassing a control) Redflags delivers an immediate nudge that corrects the behaviour on the spot. These micro interventions reinforce safer habits over time, turning awareness into action and action into measurable improvement.
Make compliance measurable
and proactive
Every interaction is captured as evidence. Redflags provides clear metrics that show how behaviours are shifting, how risk levels are trending, and when and where additional support is needed. This gives security teams a continuous, data-driven view of human risk, making it easy to demonstrate progress, prove control effectiveness, and show auditors that compliance is working in practice. With Redflags, compliance becomes proactive, measurable, and continuously improving rather than reactive and box-ticking.

Your Redflags checklist
Helping you map out the Redflags support to your compliance requirements.

Meaningful metrics that strengthen your organisation’s human risk score and highlight where attention is needed, helping you improve continuously.
Behaviour‑shaping training that builds safer habits over time, supported by real‑time nudges that correct risky actions in the moment.
Clear, actionable insights showing what your team has achieved, how workforce security posture has improved, and evidence that can feed directly into audit reporting.
How Redflags can help
Framework
- NIST Cyber Security Framework (CSF)
- NIS2
- ISO 27001
- UK Cyber Assessment Framework (CAF)
- Cyber Essentials
Content
 Specific content to teach end-users about the framework, its requirements and what it means for them
- Content to support each frameworks’ training requirements across multiple risk domains
- Address role-based, or high-risk audience training requirements by segmenting audiences and targeting content
Nudges
- Nudges to support frameworks’ training requirements across frameworks’ control topics
- Nudges drive secure behaviours to ensure you’re not just compliant, but actually driving secure behaviour change
- Address role-based, or high-risk audience training requirements, only nudging when the risky behaviour is being done
Reporting
- Trackers give visibility into behaviours related to frameworks’ control topics
- Trackers support frameworks’ evidence requirements to prove ongoing effectiveness of controls
- Insights in the Redflags web portal help you to create a measurable, ongoing picture of behaviour change to present to auditors, risk committees and boards.
Intelligent Behaviour Change. When and where it matters.
Measure human risk, nudge preemptively, prove operational impact, all without slowing people down.

Reading corner

A Guide To NIS2 and DORA Compliance for Your Financial Services in the UK
In the financial services industry, there’s little room for error when it comes to cyber behaviours. Amidst the AI boom, ...
Read article
What Risks Do AI and Copilot Tools Create for Compliance?
The rapid rise of artificial intelligence tools is reshaping how organisations work and redefining workflows. But this transition is happening...
Read article

A Hacker’s Perspective: Cyber Security Compliance and Human Risk
Glenn Wilkinson, ethical hacker and co-founder of Agger Labs: “A lot of organisations overestimate their position,” he explains. “They think...
Read article
Hear from our experts


Culture, Conduct, Compliance: How Behaviour Change Will Shape Cyber Resilience in 2026
Watch on-demand

Tech talk with Jamie Graves
Watch on-demand
BOOK A DISCOVERY CALL
Deliver both compliant and effective security awareness with Redflags® Start today.
What does real-time, in-context awareness look like? We’d love to show you!
Book a discovery call today and find out a completely new way of delivering security awareness and driving secure behaviours with Redflags
"*" indicates required fields
Beacon
Gamma Communications plc.
Laura Morgans
Global Security Governance, Risk and Compliance Manager, Dr. Martens
“We’ve customised the training to fit every language. It’s inclusive, relevant, and very quick to do.”
Industry
accolades